Artificial Intelligence

Artificial Intelligence examines how AI is reshaping enterprise technology, cybersecurity, governance, risk, and decision-making. Coverage includes generative AI, large language models, AI agents, automation, emerging capabilities, security, regulation, and organizational transformation—with a CISO focus on understanding how artificial intelligence changes both the enterprise and the security landscape.
03
Oct
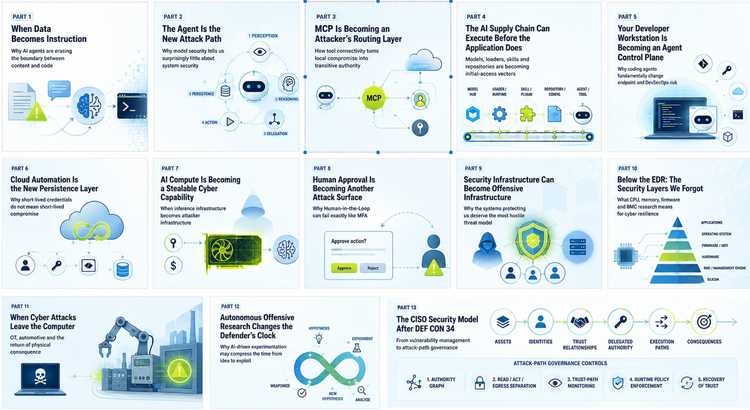
DEF CON 34 — What CISOs Should Take Away From the Hacker’s View of the Future

DEF CON 34 — What CISOs Should Take Away From the Hacker’s View of the Future

DEF CON 34 reveals a fundamental shift in cybersecurity: attackers increasingly exploit relationships, not isolated assets. This 13-part CISO series explores AI agents, MCP, identity, automation and the rise of authority-path governance.
5 min read
03
Oct
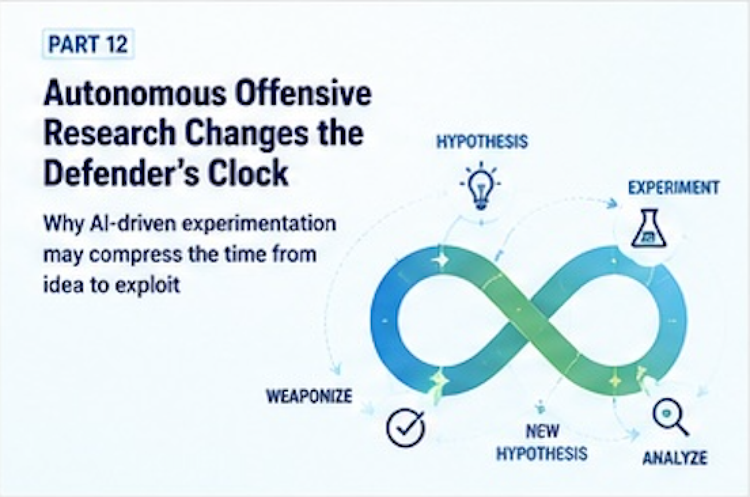
Part 12 — Autonomous Offensive Research Changes the Defender’s Clock

Part 12 — Autonomous Offensive Research Changes the Defender’s Clock

AI may not just accelerate attacks—it may automate experimentation itself. As the path from hypothesis to exploit compresses, CISOs must rethink vulnerability management, attack-path governance and the time assumptions behind modern defense.
9 min read
18
Aug
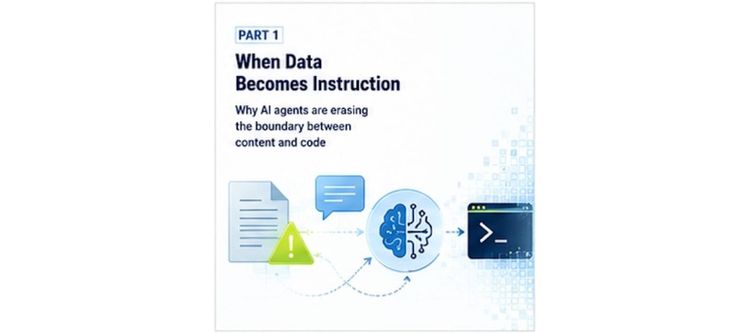
Part 1 — When Data Becomes Instruction

Part 1 — When Data Becomes Instruction

AI agents are erasing the boundary between data and instruction. DEF CON 34 shows why untrusted context can become an indirect control plane—and why CISOs must secure the entire path from meaning to authority.
15 min read
05
Aug
AI Doesn’t Need to Understand BACnet: Why Building Automation Has Entered a New Threat Era

AI Doesn’t Need to Understand BACnet: Why Building Automation Has Entered a New Threat Era

AI is transforming cyber attacks against building automation. Tasks that once required deep knowledge of BACnet, KNX or Modbus can now be accelerated by large language models, dramatically lowering the barrier to targeting smart buildings.
4 min read
03
Aug
Identity Becomes the New Security Perimeter

Identity Becomes the New Security Perimeter

The future of cybersecurity will not be secured by firewalls but by identities. Humans are becoming just one identity type among AI agents, APIs, machines and services. CISOs must rethink Identity as the primary security perimeter.
4 min read
03
Aug
Governance Failed Before Technology Did

Governance Failed Before Technology Did

Most AI-related breaches are not caused by failing models but by failing governance. Weak identity controls, unclear ownership and inconsistent oversight create the conditions attackers exploit. AI security begins with executive governance—not with technology.
4 min read
03
Aug
Detection Is Too Late

Detection Is Too Late

AI is compressing the time between vulnerability discovery and exploitation. Organizations that rely primarily on detection are reacting to attacks that have already succeeded. Prevention is no longer optional—it has become an economic necessity.
5 min read
03
Aug
AI Changed the Economics of Cybercrime

AI Changed the Economics of Cybercrime

AI is not simply creating more cyber attacks—it is fundamentally changing their economics. As attackers operate at machine speed, traditional security assumptions break down. CISOs must rethink cyber risk as an economic and governance challenge, not only a technical one.
4 min read
03
Aug
Beyond the Breach Report: Why the Real Story Is Governance, Not AI

Beyond the Breach Report: Why the Real Story Is Governance, Not AI

The IBM Cost of a Data Breach Report 2026 is more than an annual benchmark. It reveals a structural shift in cyber risk driven by AI, governance failures and organizational resilience. This series explores what CISOs should do next—not what they should buy.
4 min read
29
Jul
The CISO Governance Model

The CISO Governance Model

5 min read