Black Hat USA 2026 — The Architecture of Trust Is Changing
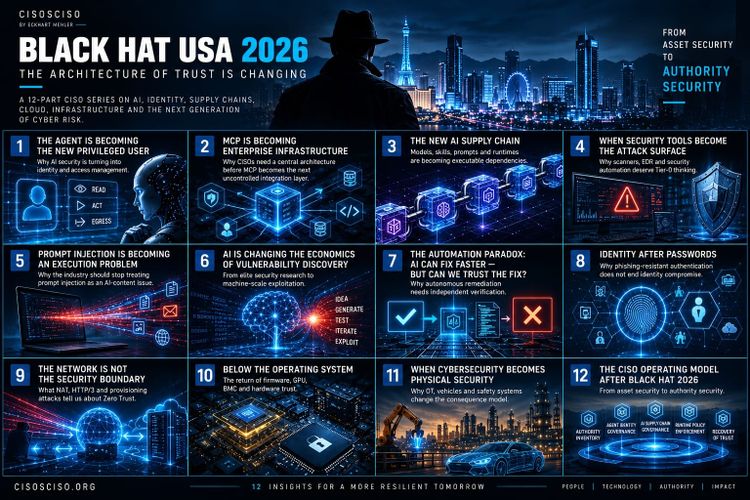
Black Hat USA 2026 points to a fundamental shift in cybersecurity: from protecting assets to governing authority. Across AI agents, MCP, identity, supply chains, cloud, hardware and OT, this 12-part CISO series explores how the architecture of trust is changing.
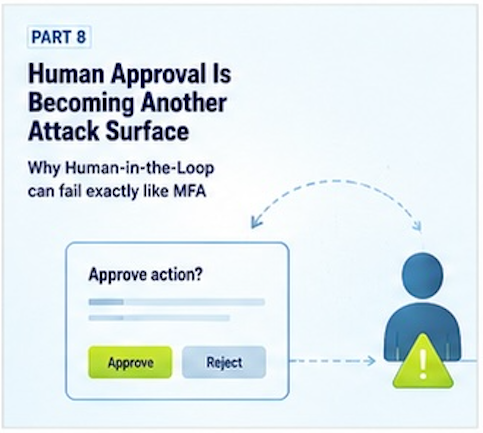
Part 8 — Human Approval Is Becoming Another Attack Surface
Human-in-the-Loop is not automatically a security control. When approvals become routine, humans stop verifying consequences and start clearing friction. Agentic AI may turn approval fatigue into the next MFA fatigue.
The Shadow AI Economy: From Shadow IT to Shadow Agency
Shadow AI is becoming Shadow Agency. At PAC Horizons 2026, I discussed how AI agents, identities, tokens and delegated authority are changing the CISO agenda — and why Least Privilege may no longer be enough.
The New AI Supply Chain
The AI supply chain no longer delivers only software. Models, prompts, skills, MCP servers and runtimes can all shape execution. CISOs must start governing not only executable code, but executable meaning.
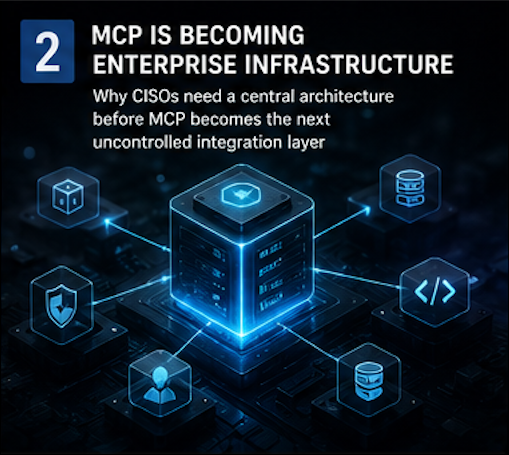
MCP Is Becoming Enterprise Infrastructure
MCP is becoming enterprise infrastructure. As AI agents gain access to tools, identities and business systems, CISOs must govern not just integration — but the authority flowing through it.
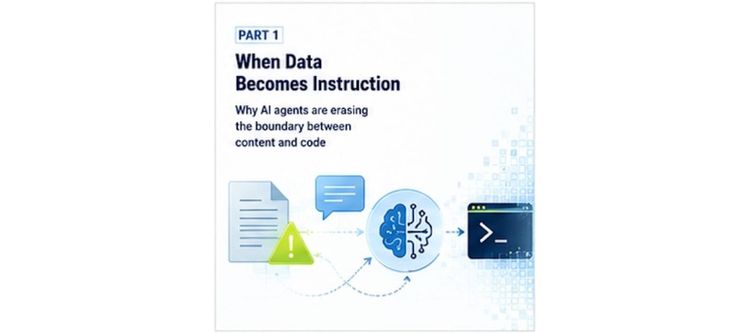
Part 1 — When Data Becomes Instruction
AI agents are erasing the boundary between data and instruction. DEF CON 34 shows why untrusted context can become an indirect control plane—and why CISOs must secure the entire path from meaning to authority.