DEF CON 34 — What CISOs Should Take Away From the Hacker’s View of the Future
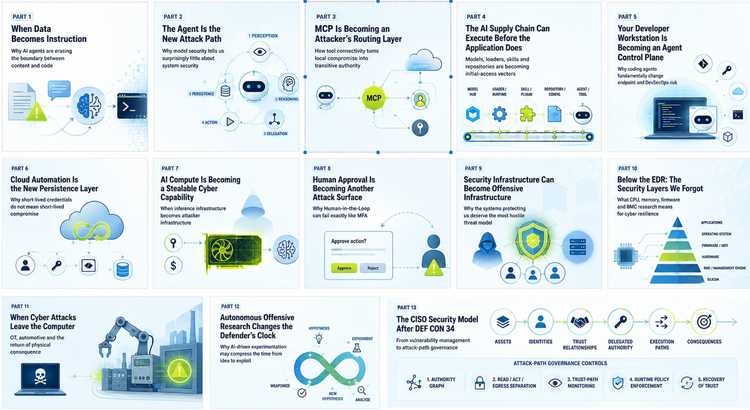
DEF CON 34 reveals a fundamental shift in cybersecurity: attackers increasingly exploit relationships, not isolated assets. This 13-part CISO series explores AI agents, MCP, identity, automation and the rise of authority-path governance.
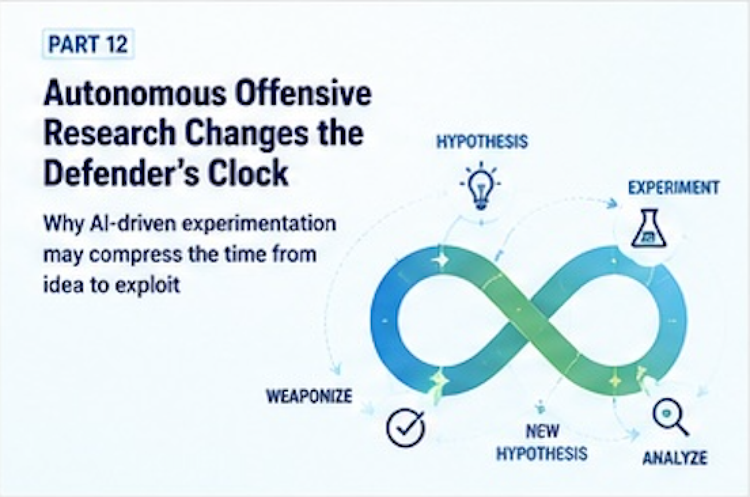
Part 12 — Autonomous Offensive Research Changes the Defender’s Clock
AI may not just accelerate attacks—it may automate experimentation itself. As the path from hypothesis to exploit compresses, CISOs must rethink vulnerability management, attack-path governance and the time assumptions behind modern defense.
Part 9 — Security Infrastructure Can Become Offensive Infrastructure
Security tools increasingly consume hostile data, interpret it with AI and act with privileged authority. DEF CON 34 showed how telemetry, evidence and agentic security workflows can be manipulated—turning the infrastructure built to defend the enterprise into an attack path.
Part 8 — Human Approval Is Becoming Another Attack Surface
Human-in-the-Loop is not automatically a security control. When approvals become routine, humans stop verifying consequences and start clearing friction. Agentic AI may turn approval fatigue into the next MFA fatigue.