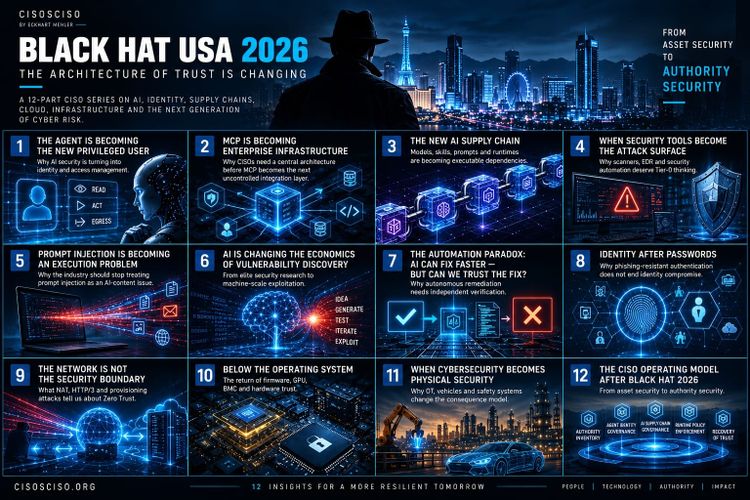
Black Hat USA 2026 — The Architecture of Trust Is Changing
Black Hat USA 2026 points to a fundamental shift in cybersecurity: from protecting assets to governing authority. Across AI agents, MCP, identity, supply chains, cloud, hardware and OT, this 12-part CISO series explores how the architecture of trust is changing.
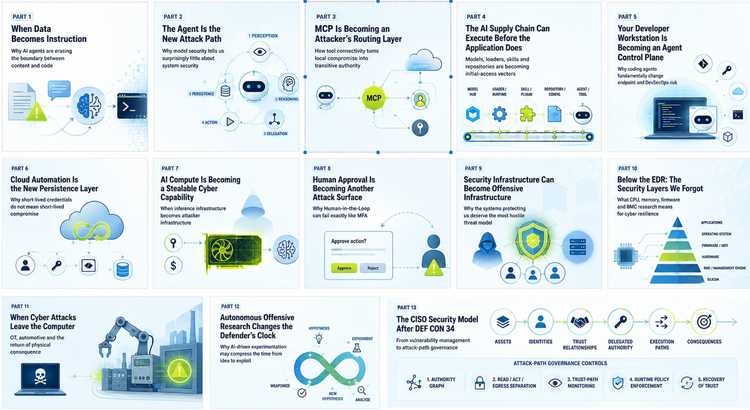
DEF CON 34 — What CISOs Should Take Away From the Hacker’s View of the Future
DEF CON 34 reveals a fundamental shift in cybersecurity: attackers increasingly exploit relationships, not isolated assets. This 13-part CISO series explores AI agents, MCP, identity, automation and the rise of authority-path governance.
Part 12 — Autonomous Offensive Research Changes the Defender’s Clock
AI may not just accelerate attacks—it may automate experimentation itself. As the path from hypothesis to exploit compresses, CISOs must rethink vulnerability management, attack-path governance and the time assumptions behind modern defense.
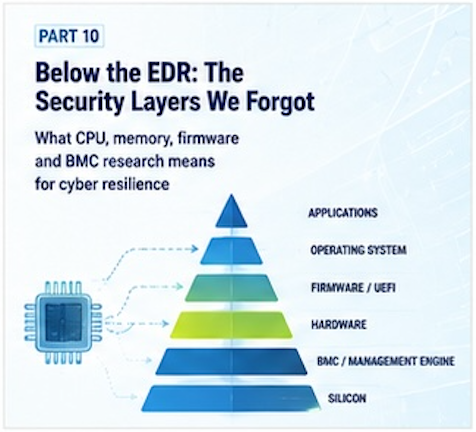
Part 10 — Below the EDR: The Security Layers We Forgot
What if reimaging a compromised server does not restore trust? DEF CON 34 hardware research exposes the layers below EDR—from firmware and BMCs to SMM, security processors and memory—forcing CISOs to rethink what cyber recovery actually means.
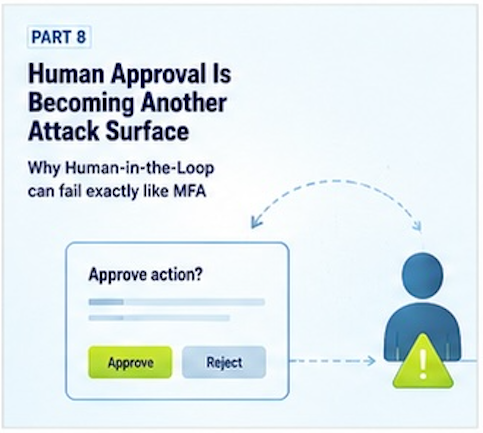
Part 8 — Human Approval Is Becoming Another Attack Surface
Human-in-the-Loop is not automatically a security control. When approvals become routine, humans stop verifying consequences and start clearing friction. Agentic AI may turn approval fatigue into the next MFA fatigue.