02
Oct
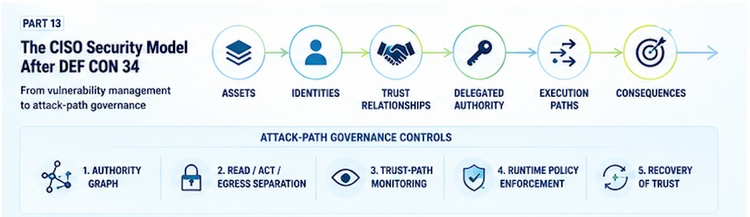
Part 13 — The CISO Security Model After DEF CON 34
DEF CON 34 exposed a fundamental shift: attackers increasingly exploit relationships, not isolated components. CISOs must move beyond assets and vulnerabilities toward governing authority paths—who can instruct, authenticate, invoke and ultimately cause what to happen.
14 min read