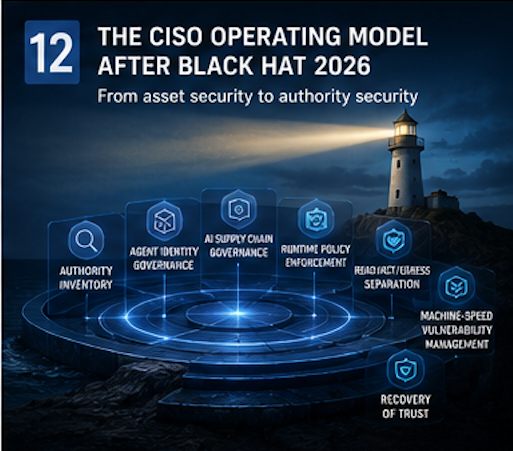
The CISO Operating Model After Black Hat 2026
Black Hat USA 2026 points to a deeper shift in security leadership: the CISO must move beyond protecting systems toward governing delegated authority — who can act, what they can cause, under which constraints, and with what consequence.
SAP Is Not a Black Box Anymore — The CISO Needs to See Inside
SAP is no longer a security black box. Sentinel, Defender and Onapsis can make SAP risk visible — but only if CISOs connect monitoring, detection and SAP-specific intelligence into one continuous assurance model.
The CISO PLAYBOOK – Leadership, Strategy, and Innovation
A curated CISO Playbook on leadership, strategy, innovation, resilience, and security culture — designed for cybersecurity leaders who must translate risk, technology, and governance into executive decisions.