The New AI Supply Chain
The AI supply chain no longer delivers only software. Models, prompts, skills, MCP servers and runtimes can all shape execution. CISOs must start governing not only executable code, but executable meaning.
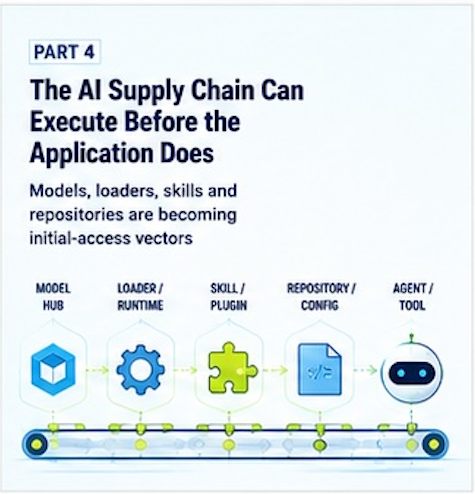
The AI Supply Chain Can Execute Before the Application Does
AI artifacts are no longer passive data. DEF CON 34 shows how models, Skills, repositories and loaders can become execution paths — forcing CISOs to rethink supply-chain security, provenance and runtime authority.
MCP Is Becoming Enterprise Infrastructure
MCP is becoming enterprise infrastructure. As AI agents gain access to tools, identities and business systems, CISOs must govern not just integration — but the authority flowing through it.
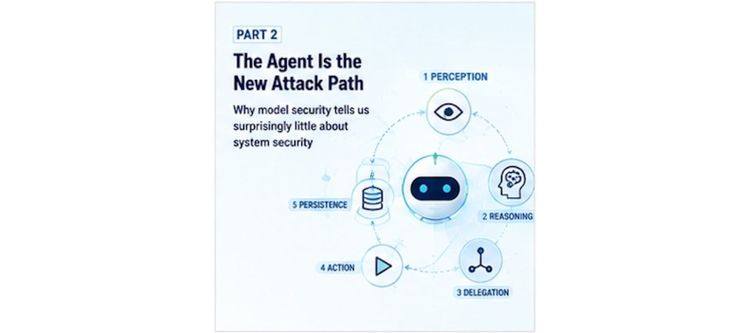
The Agent Is the New Attack Path
A safe model does not imply a safe agent. Agentic AI shifts the security problem from jailbreaks to authority: can an attacker make the system perform an authorized action for an unauthorized reason?
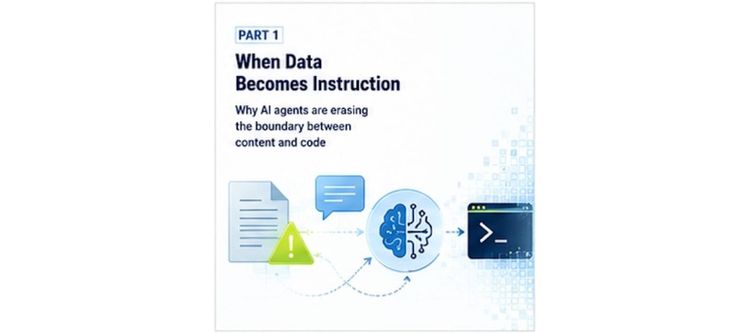
When Data Becomes Instruction
AI agents are erasing the boundary between data and instruction. DEF CON 34 shows why untrusted context can become an indirect control plane—and why CISOs must secure the entire path from meaning to authority.