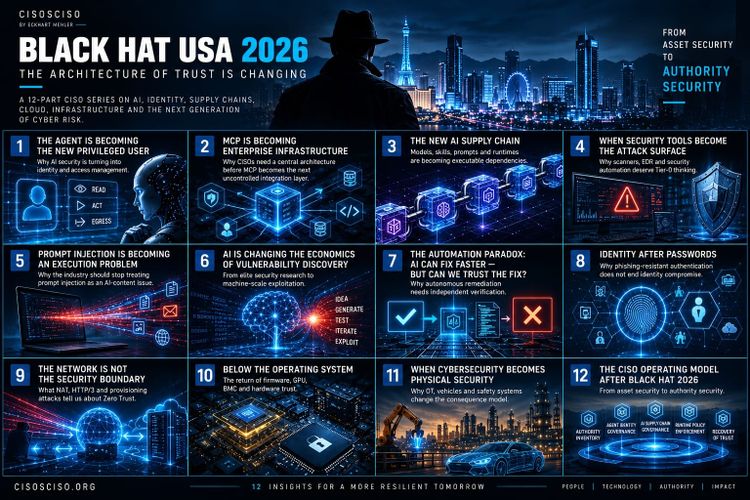
Black Hat USA 2026 — The Architecture of Trust Is Changing
Black Hat USA 2026 points to a fundamental shift in cybersecurity: from protecting assets to governing authority. Across AI agents, MCP, identity, supply chains, cloud, hardware and OT, this 12-part CISO series explores how the architecture of trust is changing.
The Enterprise of Crime: What the UNODC Threat Assessment Means for Every CISO
Cybercrime has evolved into a global industry. The UNODC Threat Assessment reveals how organized crime combines AI, identity theft, fraud and supply chains into scalable business models—and why governance, identity and operational control have become the CISO’s new strategic battlefield.
Can You Explain Why You Are Secure — Without Slides?
Cybersecurity leadership is tested when the slides disappear. This article explores why CISOs must explain security through clarity, judgment, assumptions, and ownership — not only through dashboards, heat maps, and polished board reports.