Part 9 — Security Infrastructure Can Become Offensive Infrastructure
Security tools increasingly consume hostile data, interpret it with AI and act with privileged authority. DEF CON 34 showed how telemetry, evidence and agentic security workflows can be manipulated—turning the infrastructure built to defend the enterprise into an attack path.
The Shadow AI Economy: From Shadow IT to Shadow Agency
Shadow AI is becoming Shadow Agency. At PAC Horizons 2026, I discussed how AI agents, identities, tokens and delegated authority are changing the CISO agenda — and why Least Privilege may no longer be enough.
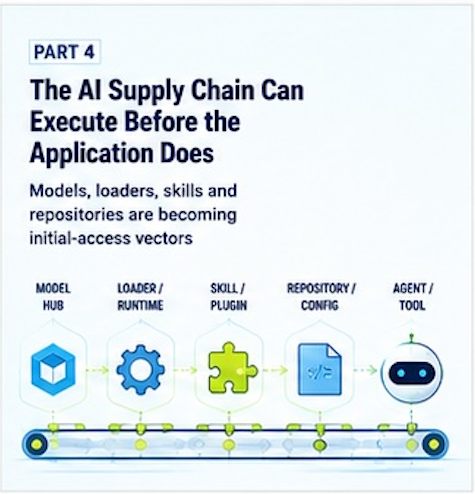
Part 4 — The AI Supply Chain Can Execute Before the Application Does
AI artifacts are no longer passive data. DEF CON 34 shows how models, Skills, repositories and loaders can become execution paths — forcing CISOs to rethink supply-chain security, provenance and runtime authority.
MCP Is Becoming Enterprise Infrastructure
MCP is becoming enterprise infrastructure. As AI agents gain access to tools, identities and business systems, CISOs must govern not just integration — but the authority flowing through it.
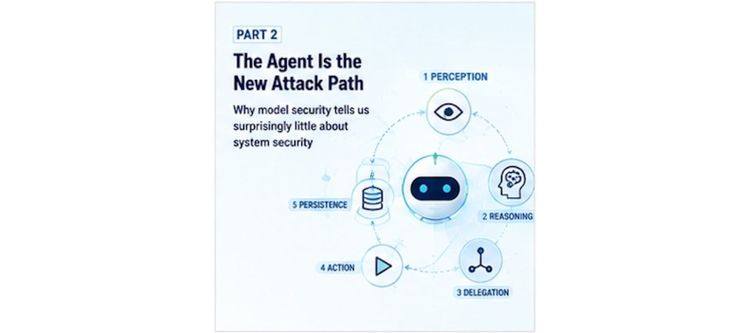
Part 2 —The Agent Is the New Attack Path
A safe model does not imply a safe agent. Agentic AI shifts the security problem from jailbreaks to authority: can an attacker make the system perform an authorized action for an unauthorized reason?