AI Security

AI Security explores the risks, architectures, controls, and governance required to secure artificial intelligence across the enterprise. Coverage includes generative and agentic AI, LLMs, models, data, identities, tools, MCP, authorization, supply chains, attacks, and emerging security architectures—with a focus on what CISOs need to understand, govern, and defend.
04
Oct
Part 8 — The CISO’s Cloud Security Agenda for 2027

Part 8 — The CISO’s Cloud Security Agenda for 2027

16 min read
04
Oct
Part 7 — From Least Privilege to Least Agency

Part 7 — From Least Privilege to Least Agency

16 min read
04
Oct
Part 6 — AI Systems Are Becoming Security Domains of Their Own

Part 6 — AI Systems Are Becoming Security Domains of Their Own

14 min read
04
Oct
Part 5 — Your Cloud Boundary Is Now Someone Else’s API

Part 5 — Your Cloud Boundary Is Now Someone Else’s API

15 min read
04
Oct
Part 4 — AI Doesn’t Replace Cyberattacks — It Compresses Them

Part 4 — AI Doesn’t Replace Cyberattacks — It Compresses Them

15 min read
04
Oct
Part 2 — Identity Is Becoming the New Cloud Control Plane

Part 2 — Identity Is Becoming the New Cloud Control Plane

Identity no longer just determines who can access the cloud. It determines who — or what — can change it. As infrastructure becomes programmable and agents gain authority, identity itself is becoming the new cloud control plane.
11 min read
04
Oct
Part 1 — The Cloud Has Changed — Our Security Model Hasn’t

Part 1 — The Cloud Has Changed — Our Security Model Hasn’t

The cloud attack surface is no longer just a collection of assets. Identity, APIs, AI agents and third parties create paths where risk emerges from relationships. Attackers already see the graph. Do defenders?
11 min read
04
Oct
The Cloud Has Changed — Our Security Model Hasn’t

The Cloud Has Changed — Our Security Model Hasn’t

Cloud security is shifting from protecting assets to governing relationships, identities and autonomous actors. This eight-part CISOsCISO series explores what the CSA Top Threats 2026 mean for CISOs — and why the next frontier is digital agency.
8 min read
03
Oct
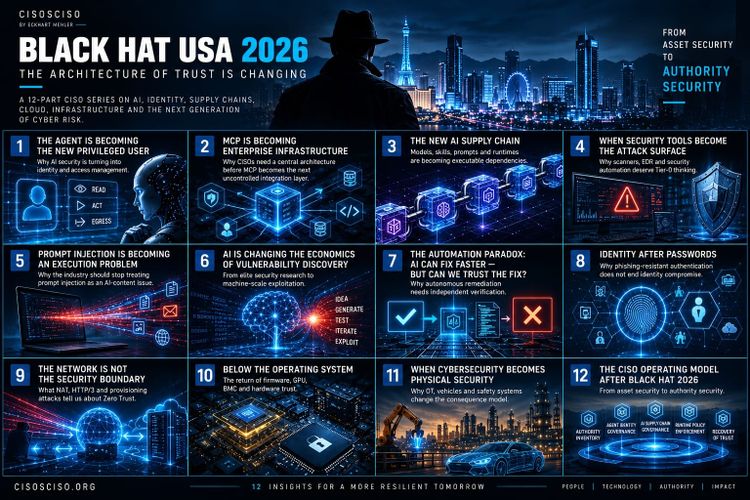
Black Hat USA 2026 — The Architecture of Trust Is Changing

Black Hat USA 2026 — The Architecture of Trust Is Changing

Black Hat USA 2026 points to a fundamental shift in cybersecurity: from protecting assets to governing authority. Across AI agents, MCP, identity, supply chains, cloud, hardware and OT, this 12-part CISO series explores how the architecture of trust is changing.
10 min read
02
Oct
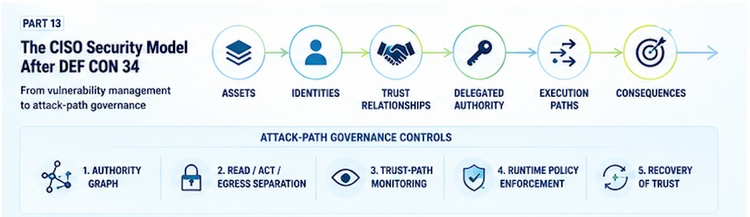
Part 13 — The CISO Security Model After DEF CON 34

Part 13 — The CISO Security Model After DEF CON 34

DEF CON 34 exposed a fundamental shift: attackers increasingly exploit relationships, not isolated components. CISOs must move beyond assets and vulnerabilities toward governing authority paths—who can instruct, authenticate, invoke and ultimately cause what to happen.
14 min read