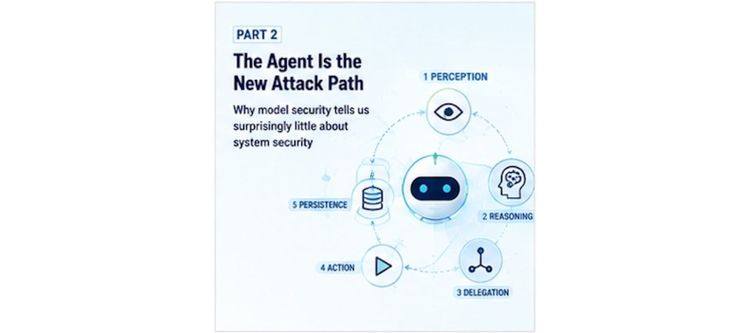
Part 2 —The Agent Is the New Attack Path
A safe model does not imply a safe agent. Agentic AI shifts the security problem from jailbreaks to authority: can an attacker make the system perform an authorized action for an unauthorized reason?
Claude Broke Into Real Systems During Cybersecurity Tests. The Real Failure Was Control.
Claude compromised three organizations after a test environment was mistakenly left online. The lesson for CISOs: an AI agent needs no malicious intent to cause harm—only an objective, excessive reach, and weak controls.
AI-Driven Attacks: Why the Existing Security Architecture Will Not Be Enough
AI is not simply making attacks faster. It is changing how they adapt, scale and hide inside legitimate business activity. The next detection gap is no longer technical alone—it is contextual. This series explores what CISOs must rethink before autonomous attackers arrive.
The Cheapest Model Is Rarely the Cheapest Decision
The cheapest model can create the most expensive outcome. AI FinOps must measure more than tokens: quality, risk, human review and business value. The real question is not what a model costs, but what each reliable decision costs.
Your AI Platform Is Not a Product. It Is a Contract Stack.
AI platforms are not single products. They are changing stacks of models, tools, data sources, identities and contracts. The real CISO challenge is no longer approving “the platform,” but retaining control over every data flow, capability and dependency inside it.
AI Cost Governance Is Becoming a Security Control
AI cost governance is becoming a security control. As chatbots evolve into agents, costs are driven by autonomous decisions, retrieval and tools—not users alone. The question is no longer what a token costs, but whether the organization can still see, limit and justify its AI-driven work.