The CISO Operating Model After Black Hat 2026
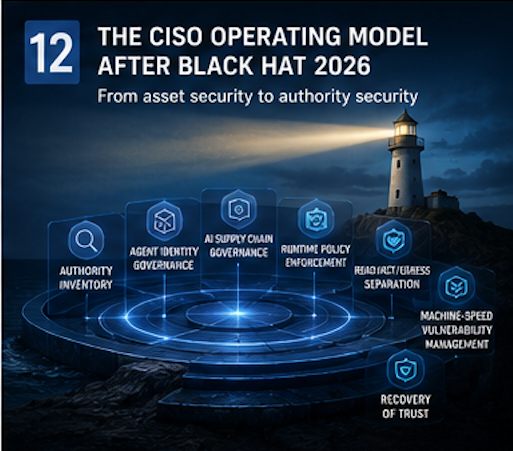
Black Hat USA 2026 points to a deeper shift in security leadership: the CISO must move beyond protecting systems toward governing delegated authority — who can act, what they can cause, under which constraints, and with what consequence.
Identity After Passwords
Phishing-resistant authentication is essential — but it does not end identity compromise. As attackers shift toward sessions, tokens, endpoints, machine identities and delegation chains, identity security must evolve from authentication assurance to authority assurance.
The New AI Supply Chain
The AI supply chain no longer delivers only software. Models, prompts, skills, MCP servers and runtimes can all shape execution. CISOs must start governing not only executable code, but executable meaning.
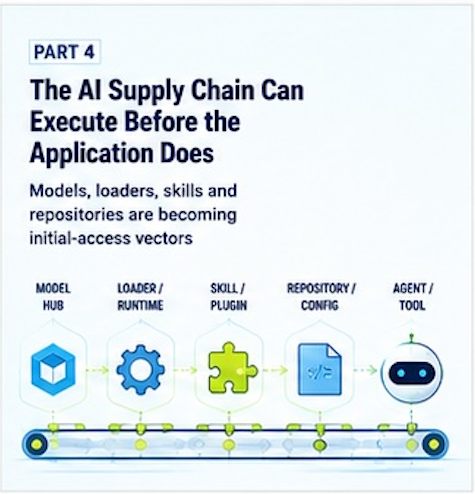
Part 4 — The AI Supply Chain Can Execute Before the Application Does
AI artifacts are no longer passive data. DEF CON 34 shows how models, Skills, repositories and loaders can become execution paths — forcing CISOs to rethink supply-chain security, provenance and runtime authority.
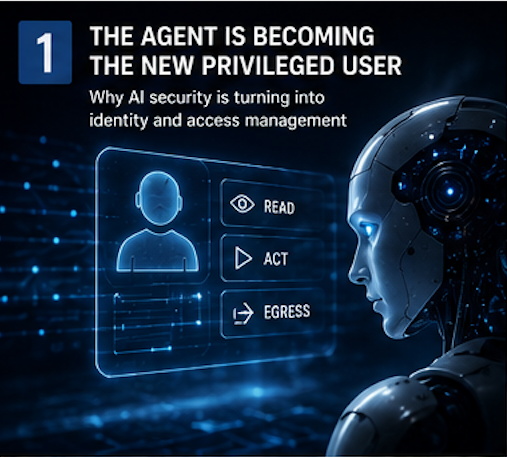
The Agent Is Becoming the New Privileged User
AI agents are becoming a new privileged identity class. The real security question is no longer what AI can know — but what it is authorized to do, through whose identity, and with what consequences.
Part 3 — MCP Is Becoming an Attacker’s Routing Layer
An AI agent’s real privilege extends far beyond its IAM permissions. MCP, managed identities and connected services create transitive authority paths that attackers can exploit—turning tool connectivity into a new routing layer for enterprise privilege.