The New AI Supply Chain
The AI supply chain no longer delivers only software. Models, prompts, skills, MCP servers and runtimes can all shape execution. CISOs must start governing not only executable code, but executable meaning.
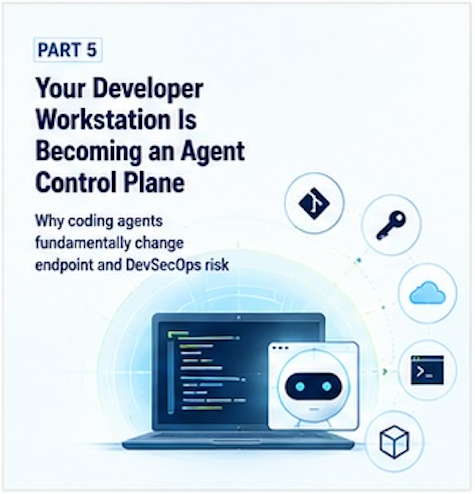
Part 5 — Your Developer Workstation Is Becoming an Agent Control Plane
Developer workstations are becoming agent control planes. Coding agents inherit identities, tools and authority—turning trusted developer environments into a new enterprise attack path.
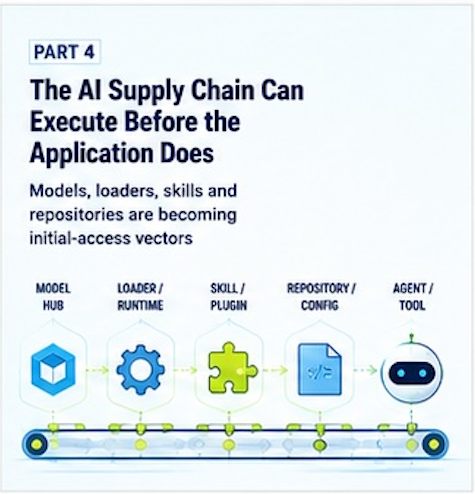
Part 4 — The AI Supply Chain Can Execute Before the Application Does
AI artifacts are no longer passive data. DEF CON 34 shows how models, Skills, repositories and loaders can become execution paths — forcing CISOs to rethink supply-chain security, provenance and runtime authority.
MCP Is Becoming Enterprise Infrastructure
MCP is becoming enterprise infrastructure. As AI agents gain access to tools, identities and business systems, CISOs must govern not just integration — but the authority flowing through it.
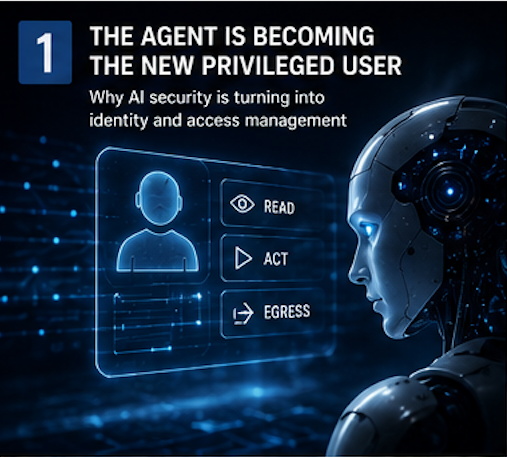
The Agent Is Becoming the New Privileged User
AI agents are becoming a new privileged identity class. The real security question is no longer what AI can know — but what it is authorized to do, through whose identity, and with what consequences.
Part 3 — MCP Is Becoming an Attacker’s Routing Layer
An AI agent’s real privilege extends far beyond its IAM permissions. MCP, managed identities and connected services create transitive authority paths that attackers can exploit—turning tool connectivity into a new routing layer for enterprise privilege.
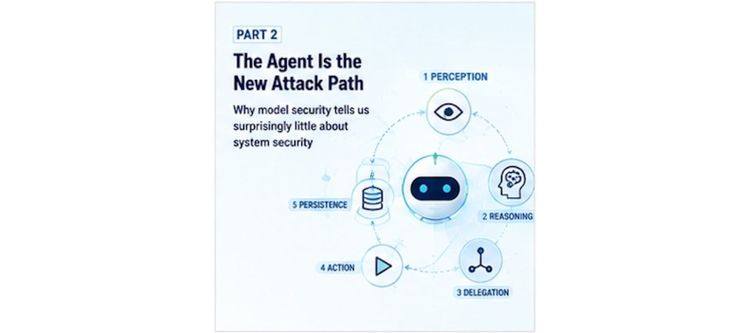
Part 2 —The Agent Is the New Attack Path
A safe model does not imply a safe agent. Agentic AI shifts the security problem from jailbreaks to authority: can an attacker make the system perform an authorized action for an unauthorized reason?
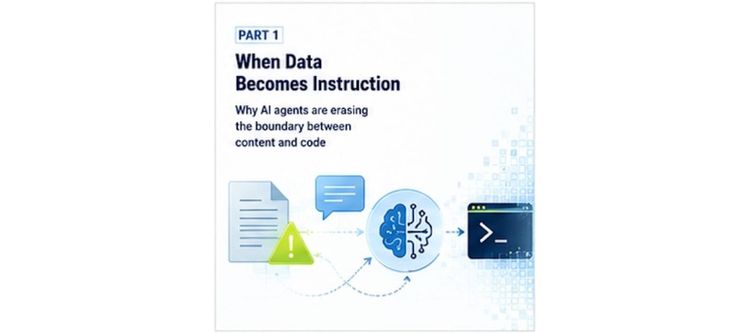
Part 1 — When Data Becomes Instruction
AI agents are erasing the boundary between data and instruction. DEF CON 34 shows why untrusted context can become an indirect control plane—and why CISOs must secure the entire path from meaning to authority.
Invisible Lies: Why Sensor Manipulation May Become the Most Dangerous Attack on Smart Buildings
Smart buildings trust their sensors. Attackers know it. By manipulating environmental data instead of software, they can influence AI, automation and human decisions without triggering traditional cyber defenses.