From Facility Management to Cyber-Physical Resilience
Part 9 of the series
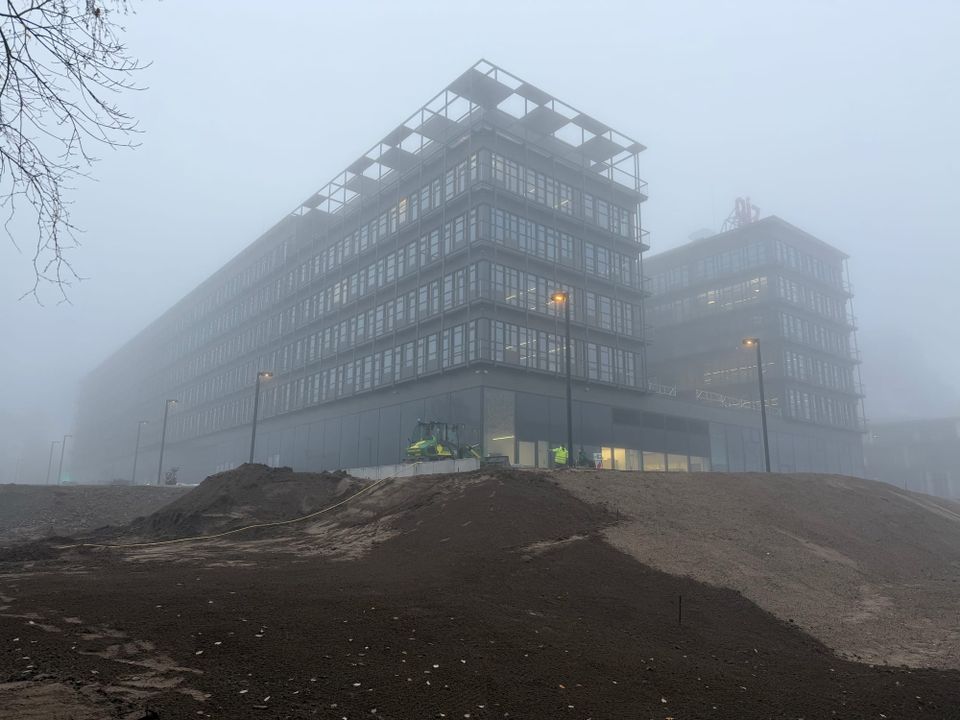
The Building Is Now Part of the Attack Surface
By Eckhart Mehler for CISOsCISO — a perspective on cybersecurity leadership, governance and the decisions that determine whether organizations retain control.
Every transformation begins with a change in perspective.
For decades, organisations viewed buildings as operational infrastructure.
Necessary.
Expensive.
Important.
But fundamentally separate from information security.
That perspective no longer reflects reality.
Modern buildings have evolved into cyber-physical platforms.
They process information.
They authenticate identities.
They exchange data.
They depend on cloud services.
They interact with enterprise networks.
They rely on software.
Most importantly, they directly influence business continuity.
The question is therefore no longer whether Facility Management should become part of cybersecurity.
The question is whether organisations are prepared to govern resilience across both worlds.
The End of Functional Silos
The traditional organisational model was logical.
Facility Management maintained buildings.
IT operated technology.
Corporate Security protected people.
The CISO governed information security.
Business Continuity prepared for disruption.
Each discipline optimised its own responsibilities.
The problem was never the people.
The problem was the boundaries.
Attackers do not distinguish between organisational departments.
Neither do cascading failures.
A compromised supplier credential can disable access control.
An unavailable access-control system prevents employees from entering.
Delayed access disrupts business operations.
Business disruption becomes an executive issue.
One event.
Four departments.
One enterprise risk.
The New Definition of Infrastructure
Infrastructure used to mean physical assets.
Today it includes:
- digital platforms,
- cloud services,
- operational technology,
- identity ecosystems,
- building automation,
- suppliers,
- remote maintenance,
- data flows,
- analytics,
- software-defined controls.
Infrastructure is no longer defined by concrete and steel.
It is defined by dependency.
Anything the organisation depends on becomes part of its resilience architecture.
Resilience Is Not Availability
Many executive discussions still equate resilience with uptime.
That definition is incomplete.
True cyber-physical resilience includes:
- operational continuity,
- secure identities,
- trusted suppliers,
- recoverable systems,
- resilient architecture,
- governance clarity,
- informed decision-making,
- adaptive incident response,
- lifecycle security.
Availability measures whether something is working.
Resilience measures whether the organisation can continue operating when something is no longer working.
That difference matters.
Cyber-Physical Risk Is Enterprise Risk
Boards often receive separate reports.
Cybersecurity reports digital threats.
Facility Management reports operational issues.
Corporate Security reports physical incidents.
Business Continuity reports recovery readiness.
The board sees multiple dashboards.
Attackers see one organisation.
Enterprise resilience begins when reporting reflects operational reality rather than organisational structure.
Executives should not have to combine fragmented reports to understand a single risk.
Governance should already have done that.
The Evolution of the CISO
The role of the CISO is changing.
Historically, CISOs focused primarily on:
- networks,
- endpoints,
- identities,
- applications,
- information.
Tomorrow’s CISO must also understand:
- operational technology,
- physical infrastructure,
- supplier ecosystems,
- engineering dependencies,
- enterprise resilience,
- cyber-physical governance.
This does not mean becoming a facility engineer.
It means becoming an enterprise risk leader.
The CISO’s greatest contribution is not technical expertise.
It is governance.
The Evolution of Facility Management
Facility Management is also changing.
Buildings increasingly operate as intelligent environments.
Facility leaders now manage:
- connected devices,
- software platforms,
- cloud services,
- identity-dependent access,
- operational data,
- digital maintenance,
- supplier ecosystems.
Cybersecurity therefore becomes part of operational excellence.
Not because Facility Management has become an IT department.
But because buildings have become digital systems.
Governance Becomes the Competitive Advantage
Technology alone will not determine which organisations become resilient.
Governance will.
The organisations that succeed will establish:
- common risk language,
- shared asset visibility,
- integrated identity governance,
- coordinated incident response,
- unified supplier governance,
- lifecycle security,
- executive transparency,
- cross-functional accountability.
These capabilities cannot be purchased.
They must be built.
Measuring What Matters
Traditional metrics often reinforce organisational silos.
Facility Management measures:
- maintenance performance,
- energy consumption,
- equipment availability.
Cybersecurity measures:
- vulnerabilities,
- incidents,
- patching,
- phishing,
- identity risk.
Cyber-physical resilience requires new questions.
For example:
- How many connected building systems are fully inventoried?
- Which operational technologies remain unsupported?
- How many suppliers possess privileged building access?
- Which building systems report security logs to the SOC?
- How quickly can physical identities be revoked?
- How many critical facilities have tested cyber-physical incident plans?
- Which construction projects include Security by Design from the planning phase?
These metrics describe resilience—not departments.
Culture Determines Success
Technology can connect systems.
Only culture connects organisations.
Successful integration depends upon:
- mutual respect,
- shared vocabulary,
- executive sponsorship,
- transparent accountability,
- common objectives.
Cybersecurity must understand operational realities.
Facility Management must understand cyber risk.
Neither discipline succeeds by educating the other.
They succeed by learning from one another.
The Board’s Responsibility
Executive management ultimately determines organisational priorities.
If cyber-physical resilience remains absent from board discussions, investment priorities will follow.
If resilience becomes a strategic objective, procurement changes.
Project governance changes.
Supplier management changes.
Incident response changes.
Leadership determines whether resilience becomes an organisational capability—or merely another technical initiative.
Looking Ahead
Artificial Intelligence.
Autonomous building management.
Predictive maintenance.
Digital twins.
Smart campuses.
Connected cities.
These developments will further increase the convergence of physical and digital infrastructure.
Every innovation introduces opportunity.
Every innovation also expands governance requirements.
The organisations that adapt early will manage complexity.
The organisations that delay will inherit it.
The Future ISMS
The ISMS of the future will not govern information alone.
It will increasingly govern trust.
Trust in:
- identities,
- suppliers,
- operational technology,
- cloud platforms,
- physical infrastructure,
- organisational decision-making.
Its purpose will remain unchanged.
To ensure that business objectives can be achieved despite uncertainty.
Only the scope of uncertainty is expanding.
Conclusion
This series began with a simple observation.
The building has become part of the attack surface.
It ends with a broader conclusion.
The building has become part of enterprise resilience.
Facility Management is no longer simply responsible for maintaining infrastructure.
It helps maintain trust.
The CISO is no longer responsible only for protecting information.
The role increasingly protects the organisation’s ability to operate safely in a connected world.
Neither discipline can achieve that objective alone.
Cyber-physical resilience is not another security programme.
It is a new management discipline.
One that connects technology, people, governance and operations into a single resilience strategy.
Because organisations will not be measured by how well they protect their networks.
They will be measured by how well they continue operating when every connected system—digital or physical—is placed under pressure.
That is the future of enterprise security.
And it has already begun.
Publication Note & Disclaimer
This article reflects my personal professional perspective and does not represent the official policy or position of my employer. Drafting and editorial refinement may have been supported by commercially available AI-assisted tools. The analysis, conclusions and final curation are entirely my own.
For information regarding image credits, copyrights, trademarks and other intellectual property rights, please refer to the Imprint.

Member discussion